Quantstamp Audits Layer 1 Blockchains


Quantstamp has secured over 5 billion USD in digital assets and provided security services for over 130 organizations including startups, foundations, and enterprises. Apart from securing the applications that run on blockchain platforms, we also offer security services for base layer protocols. Our experience with base layer protocols includes ETH2, Avalanche, and Cardano. For ETH2, we audited the Prysm client by Prysmatic Labs and we are currently auditing the Teku client by ConsenSys.
In this post, we describe what goes into a Layer 1 audit and highlight some of the unique mechanisms we have worked with.
The Consensus Layer
Quantstamp searches for bugs that may prevent Layer 1 networks from reaching consensus. For a network to be in consensus, nodes of a specific network need to be in agreement about the latest state of that network. For a distributed network to be successful, consensus disruptions must be rare because they can make the network unusable for a time.
ETH2, Cardano, and Avalanche each have a unique protocol for producing consensus. ETH2 and Cardano both use proof-of-stake (PoS): however, ETH2 has a PoS model that incentivizes good behavior through slashing, while Cardano uses a delegated proof-of-stake model without slashing. Cardano’s consensus model is referred to as “delegated proof-of-stake” because users delegate their right to validate transactions to a stake pool operator in exchange for a portion of that pool’s rewards.
Quantstamp looks for vulnerabilities that interfere with consensus and leave networks susceptible to attacks including, but not limited to:
- Unwarranted slashing
- Blockchain state corruption
- Eclipse attacks
- Denial of service attacks
- Network partition
- Channel eavesdropping
- Socket stress attacks
- Disk space exhaustion attacks
- Connection reset attacks
- Issues with file permissions
- Cheating the consensus due to logical errors
The Ledgers
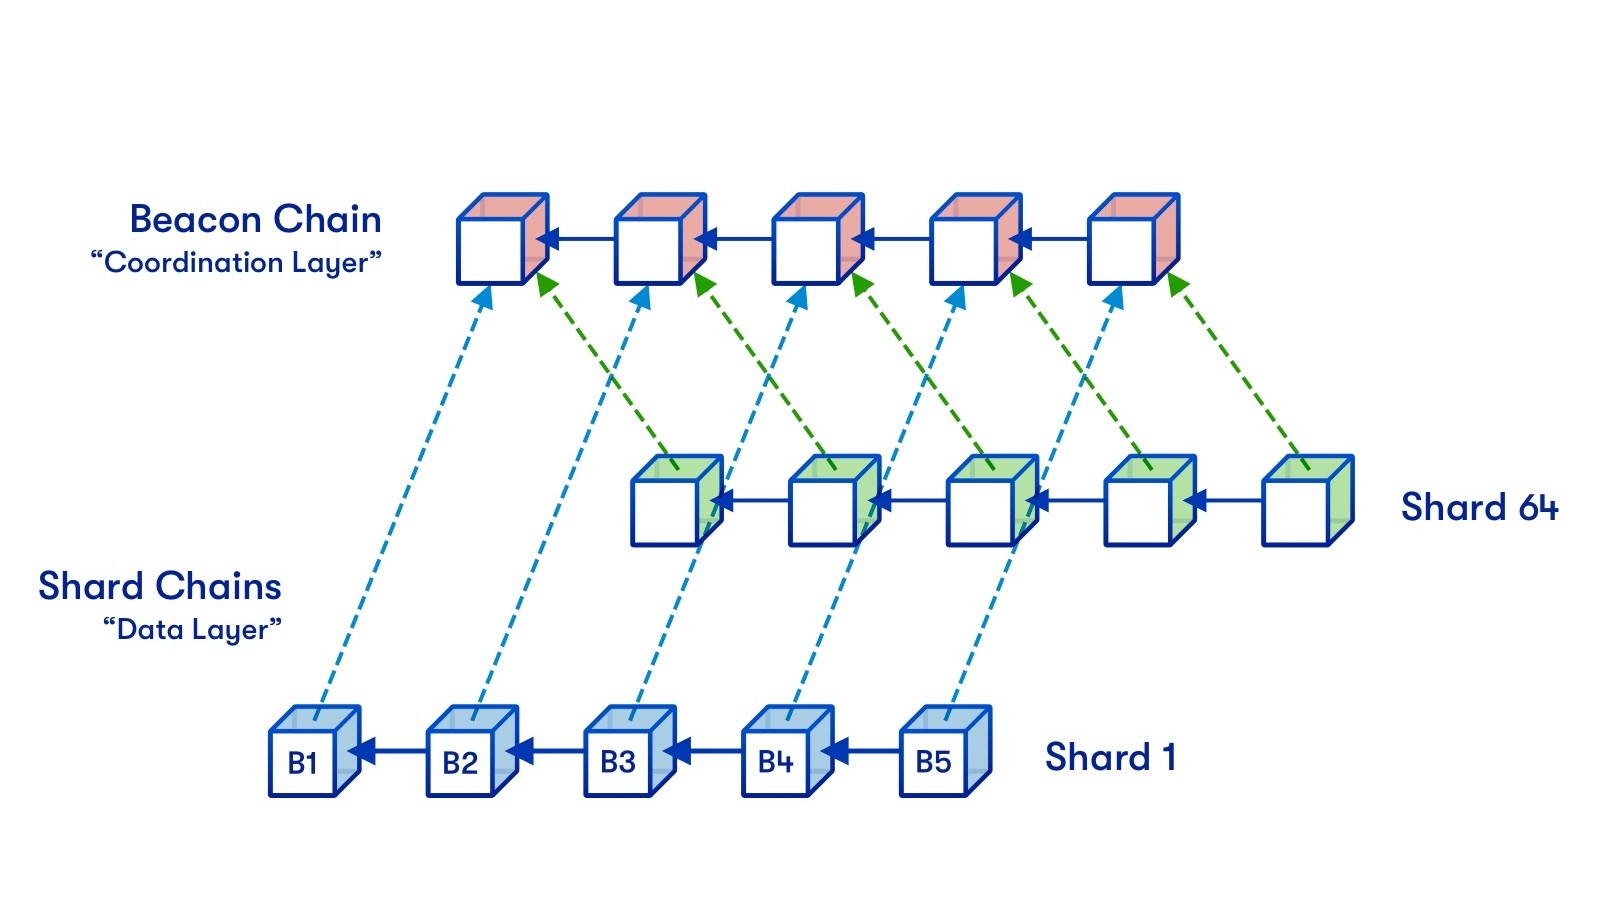
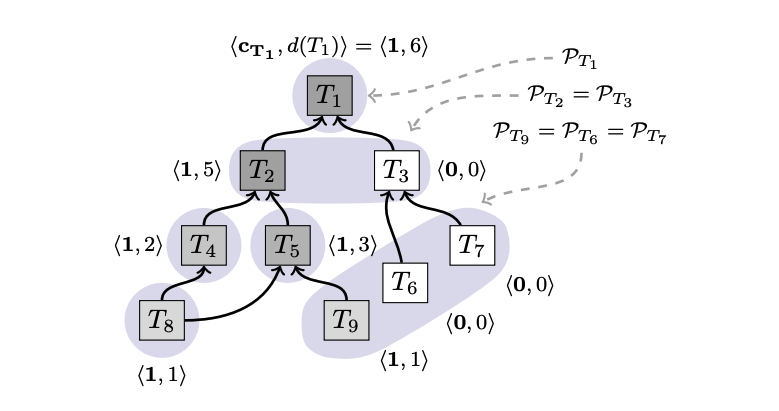
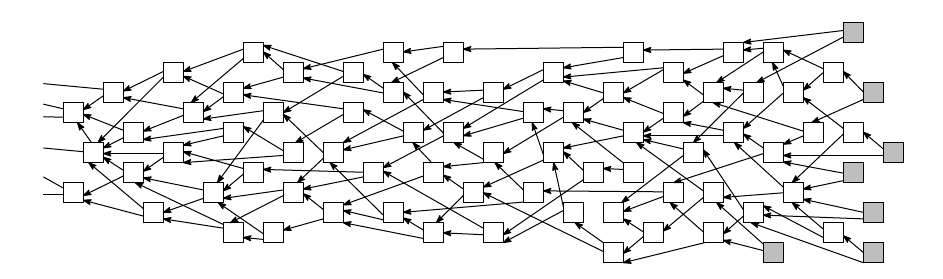
The Layer 1 protocols we have secured do not only differ in how they achieve consensus, they also differ in how they store their data. Avalanche’s ledger is actually not a blockchain but a directed acyclic graph. Cardano and ETH2 use blockchains. Quantstamp audited ETH2’s Beacon Chain, the blockchain at the heart of ETH2’s future sharded ledger system. Quantstamp ensures that the data stored in these ledgers is immutable, honest, and free of vulnerabilities.
User-Facing Applications
Organizations seeking a Layer 1 audit also need security for the user-facing applications that help non-technical users interact with the blockchain. For Cardano, Quantstamp also audited the Daedalus wallet in order to secure user private keys and funds.